Home

Menu

Close
What is the Notice of Privacy Practices Protecting Your Data in the AI Age
Published:
September 19, 2026
Introduction: Why the Notice of Privacy Practices Matters Now
In 2026, data is everywhere, and how it is handled matters more than ever. We share our personal information daily, whether with a doctor, a shopping website, or a government service. But do you truly know what happens to your data once it's collected? This is where understanding what is the notice of privacy practices becomes super important. It's not just a boring document; it's a key tool for keeping your information safe and for building trust in our digital world.
At its heart, the Notice of Privacy Practices is a clear document that tells you how an organization plans to use and share your personal information. Think of it as a promise from the organization to you about your data. For healthcare, this notice is a requirement under a law called HIPAA. It explains how your protected health information, or PHI, may be used without your direct permission and what situations need your explicit say-so. More than that, it outlines your rights over your own health records, like being able to see them or ask for changes. The U.S. Department of Health and Human Services provides guidance on these notices, making sure they are easy to understand for everyone involved in healthcare interactions Notice of Privacy Practices for Protected Health Information.
Today, for large companies, government offices, and even new AI teams, the Notice of Privacy Practices is about more than just following rules. It's a big part of how they manage trust and risk. In an age where news about data problems is common, like the advance auto parts data breach settlement or the canva cyber attack, keeping customer data safe is a must. Failing to protect information can lead to big problems, including legal actions known as privacy torts, which are lawsuits about privacy violations.
For organizations, a strong privacy notice is a bedrock for ethical data handling. It ensures that the information they collect, including valuable proprietary data meaning to their operations, is used responsibly. This is especially true for AI development, where systems need high-quality, ethically sourced data to be trustworthy. Without clear practices and transparency, AI systems might learn from distorted or poorly collected data, which can lead to bad results. Building trustworthy AI requires careful attention to how data is gathered and protected from the very beginning. To ensure AI systems are built on strong, ethical foundations, organizations must secure ethical AI with trustworthy data services.
Overview: What the Notice Typically Covers
So, if a strong privacy notice is so important, especially for today's AI systems, what does it actually contain? When you read a notice of privacy practices, you'll usually find several key pieces of information that explain how an organization handles your personal data. These documents are designed to be clear and easy to understand, even if they cover complex topics.
Here's what a good notice will generally tell you:
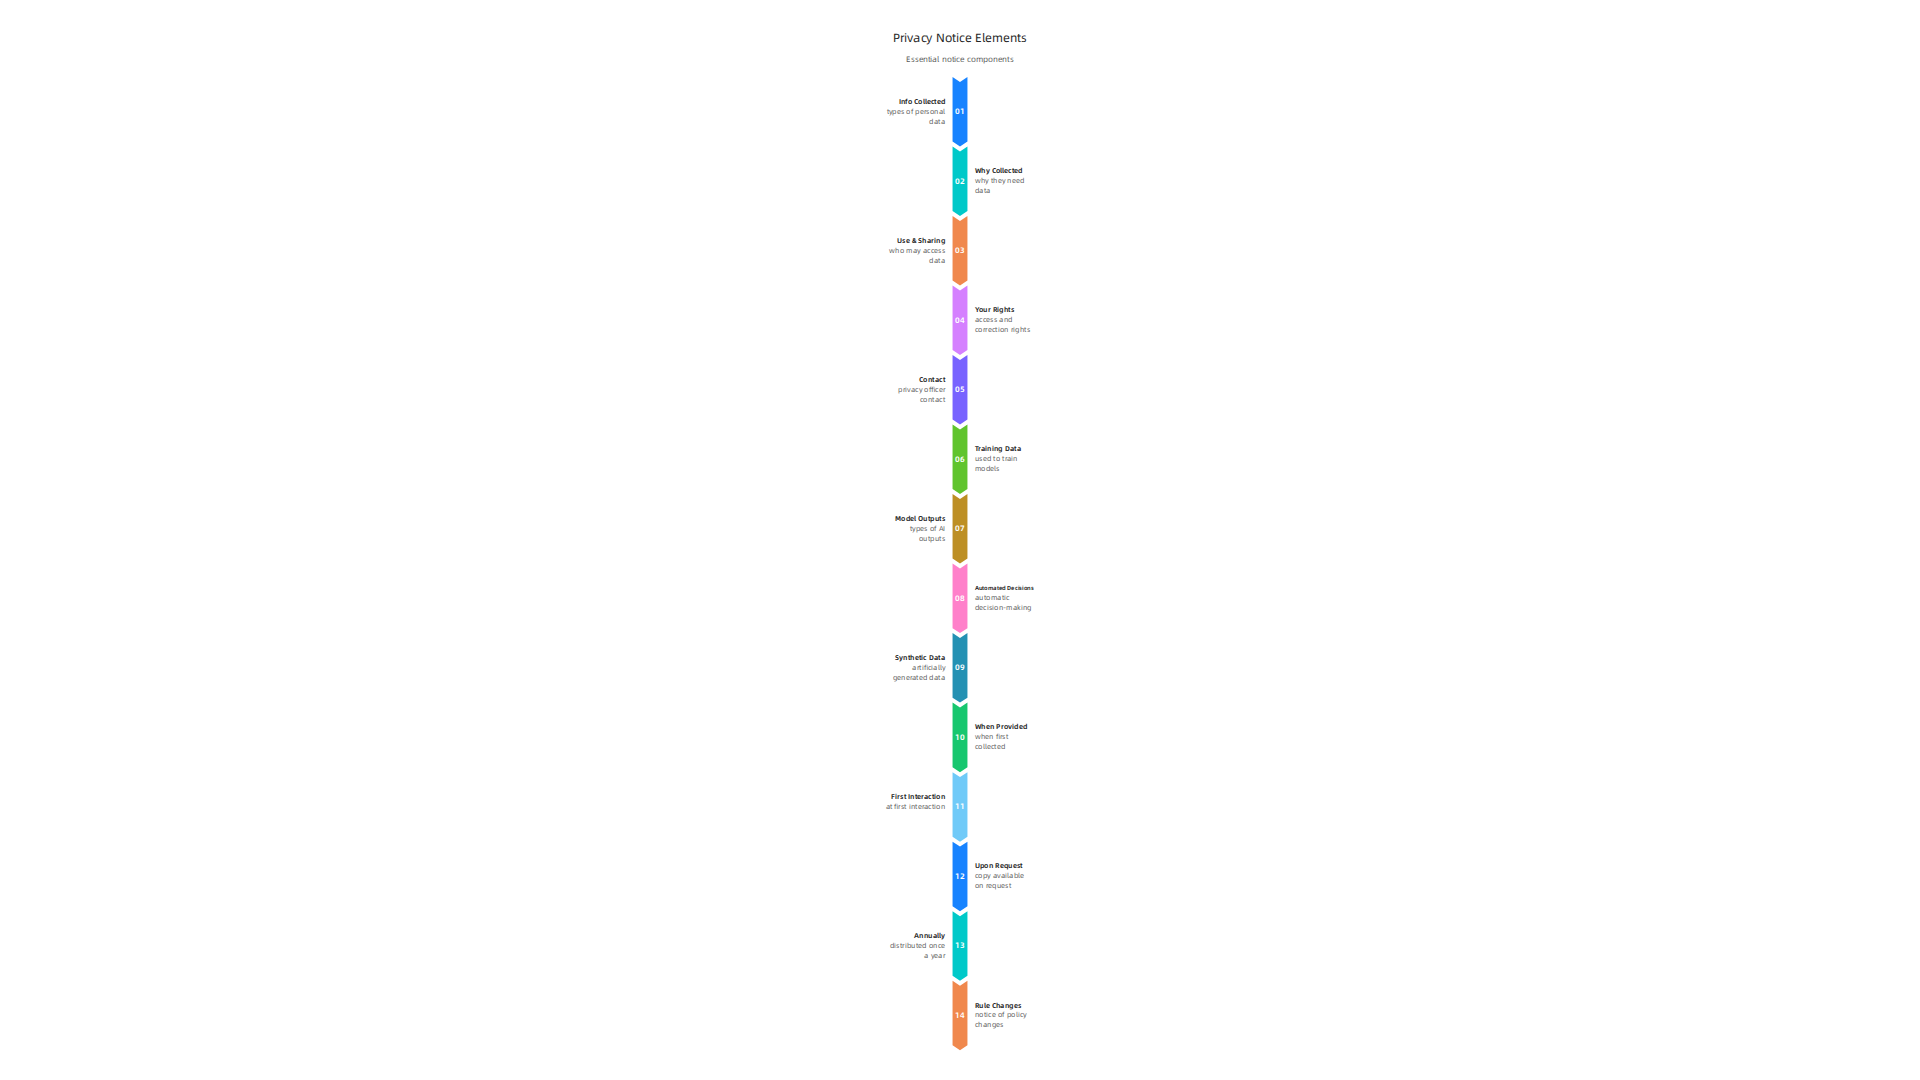
- What information is collected: This part explains what types of personal data the organization gathers. For example, a doctor's office collects your health records, while a website might collect your browsing history or email address.
- Why the information is collected (purpose): The notice will tell you why they need your data. Is it for your medical treatment? To process your online order? To improve their services or build new AI tools? The reason for collecting your data should be clear.
- How the information is used and shared: This is a big one. It explains who might see your data, both inside and outside the organization. For healthcare, this might include sharing your information with other doctors involved in your care or with your insurance company for payment Notice of Privacy Practices for Individuals. For other companies, it might involve sharing data with partners to improve services or for marketing.
- Your rights over your data: A crucial part of what is the notice of privacy practices is explaining your rights. You usually have the right to see your information, ask for changes, or even request that some data not be shared in certain ways. Organizations also must tell you how to complain if you feel your privacy has been violated. The U.S. Department of Health and Human Services offers valuable insights into these administrative requirements Administrative Requirements.
- Who to contact: The notice will provide contact details for the organization's privacy officer or department, so you know who to talk to if you have questions or concerns.
These common elements are key to transparency, and you can find a helpful checklist for crafting an effective privacy notice How to write a privacy notice and what goes in it.
How Notices Vary by Sector
While the basic idea remains the same, how a notice of privacy practices is put together can change a lot depending on the type of organization.
This is very important for large organizations to understand, especially when they manage their valuable proprietary data meaning to their business operations.
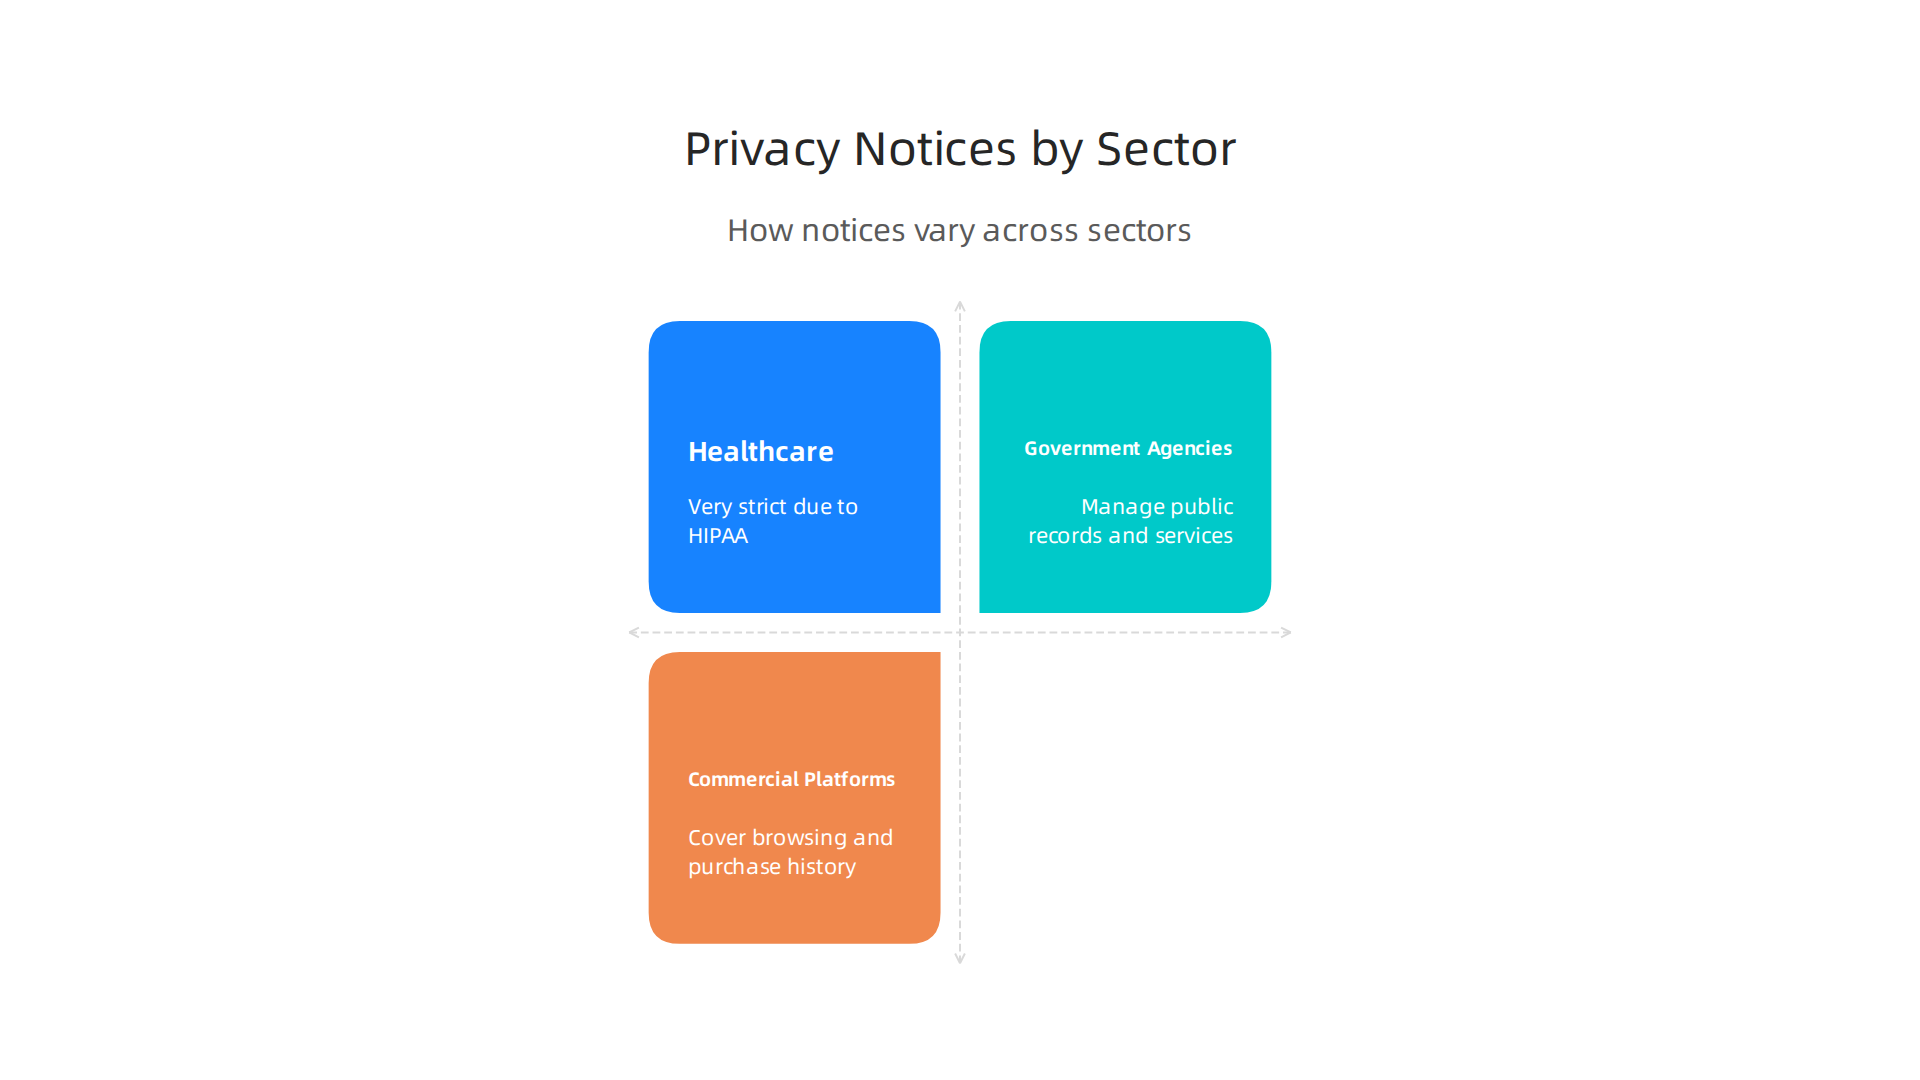
- Healthcare: These notices are very strict due to laws like HIPAA. They focus heavily on Protected Health Information (PHI), detailing how it's used for treatment, payment, and healthcare operations. They must also clearly outline patient rights, such as accessing medical records or asking for corrections, as detailed in the HIPAA Notice of Privacy Practices New Download for 2026 Update.
- Government Agencies: Government privacy notices often deal with public records, citizen services, and national security data. They explain how information is collected for official duties, how it's protected, and what rights citizens have regarding their data when interacting with government services.
- Commercial Platforms (like social media or online stores): These notices, often called privacy policies, cover a wide range of personal data, from browsing habits to purchase history. They also explain how data is used for targeted ads, personalizing user experience, and improving products. For businesses creating AI, their privacy notices in 2026 must now specifically address how AI systems use data, including what prompts or inputs are collected, how outputs are generated, and whether this data is used for training AI models AI Privacy Policy: An Informational Guide for Businesses in 2026. This extra layer of detail helps build user trust and ensures ethical data handling, which is crucial for organizations aiming to secure ethical AI with trustworthy data services.
Understanding these differences matters because it helps large organizations not only follow the law but also build trust with their customers and the public. A well-crafted privacy notice shows a commitment to responsible data stewardship, preventing misunderstandings and fostering a more ethical digital environment.
Understanding these differences matters because it helps large organizations not only follow the law but also build trust with their customers and the public. A well-crafted privacy notice shows a commitment to responsible data stewardship, preventing misunderstandings and fostering a more ethical digital environment.
Legal Requirements: Statutes, Regulations, and Standards That Govern Notices
When we talk about what is the notice of privacy practices, we're really talking about rules and laws that make sure companies and groups handle your personal information carefully. Many different laws make it a must for organizations to give you these notices. These rules help everyone understand how their data is used, especially in 2026.
Here are some main laws that require privacy notices:
- HIPAA (Health Insurance Portability and Accountability Act): This is a big one for healthcare. If you go to a doctor or use a health plan, they must give you a privacy notice. This notice explains how your health information can be used and shared. It also tells you about your rights, like getting a copy of your medical records. The U.S. Department of Health and Human Services provides helpful guidance, including Model Notices of Privacy Practices to follow. It is important to know that in 2026, all organizations covered by HIPAA must update their notices. There was a big federal deadline in February 2026 to make sure these notices include new rules, especially about specific health information requirements HIPAA NPP Requirements in 2026.
- FERPA (Family Educational Rights and Privacy Act): This law protects the privacy of student education records. Schools, from elementary to college, must give parents and eligible students an annual notice about their rights. These rights include seeing student records and asking for changes. The Department of Education offers guidance on FERPA | Protecting Student Privacy and annual notices for schools. They even provide a letter to schools about their FERPA obligations each year.
These laws show how important it is for organizations to be open about their data practices. They don't just tell you what an organization can do, but also what your rights are. This means you often have the power to say yes or no to how your data is used. For example, some notices explain that you need to give your consent for certain types of data sharing. These notices also set out the administrative obligations for organizations, meaning they have to have clear processes for giving out notices and handling complaints.
Keeping up with these rules helps organizations protect data better. It also helps build trust, especially as we deal with new technologies like AI. Knowing how your data is protected under law can help you feel more secure. This is also important for large organizations when they consider how to best handle their security systems and access controls for all their sensitive information. They often need clear guidelines, much like a security classification guide master data protection and AI access.
Delivery and Timing: When Notices Must Be Provided
Knowing what is the notice of privacy practices also means understanding when and how you should get it. Organizations can't just keep these notices hidden. They have to make sure you see them at important times.
Here are the main ways and times you usually get a privacy notice:
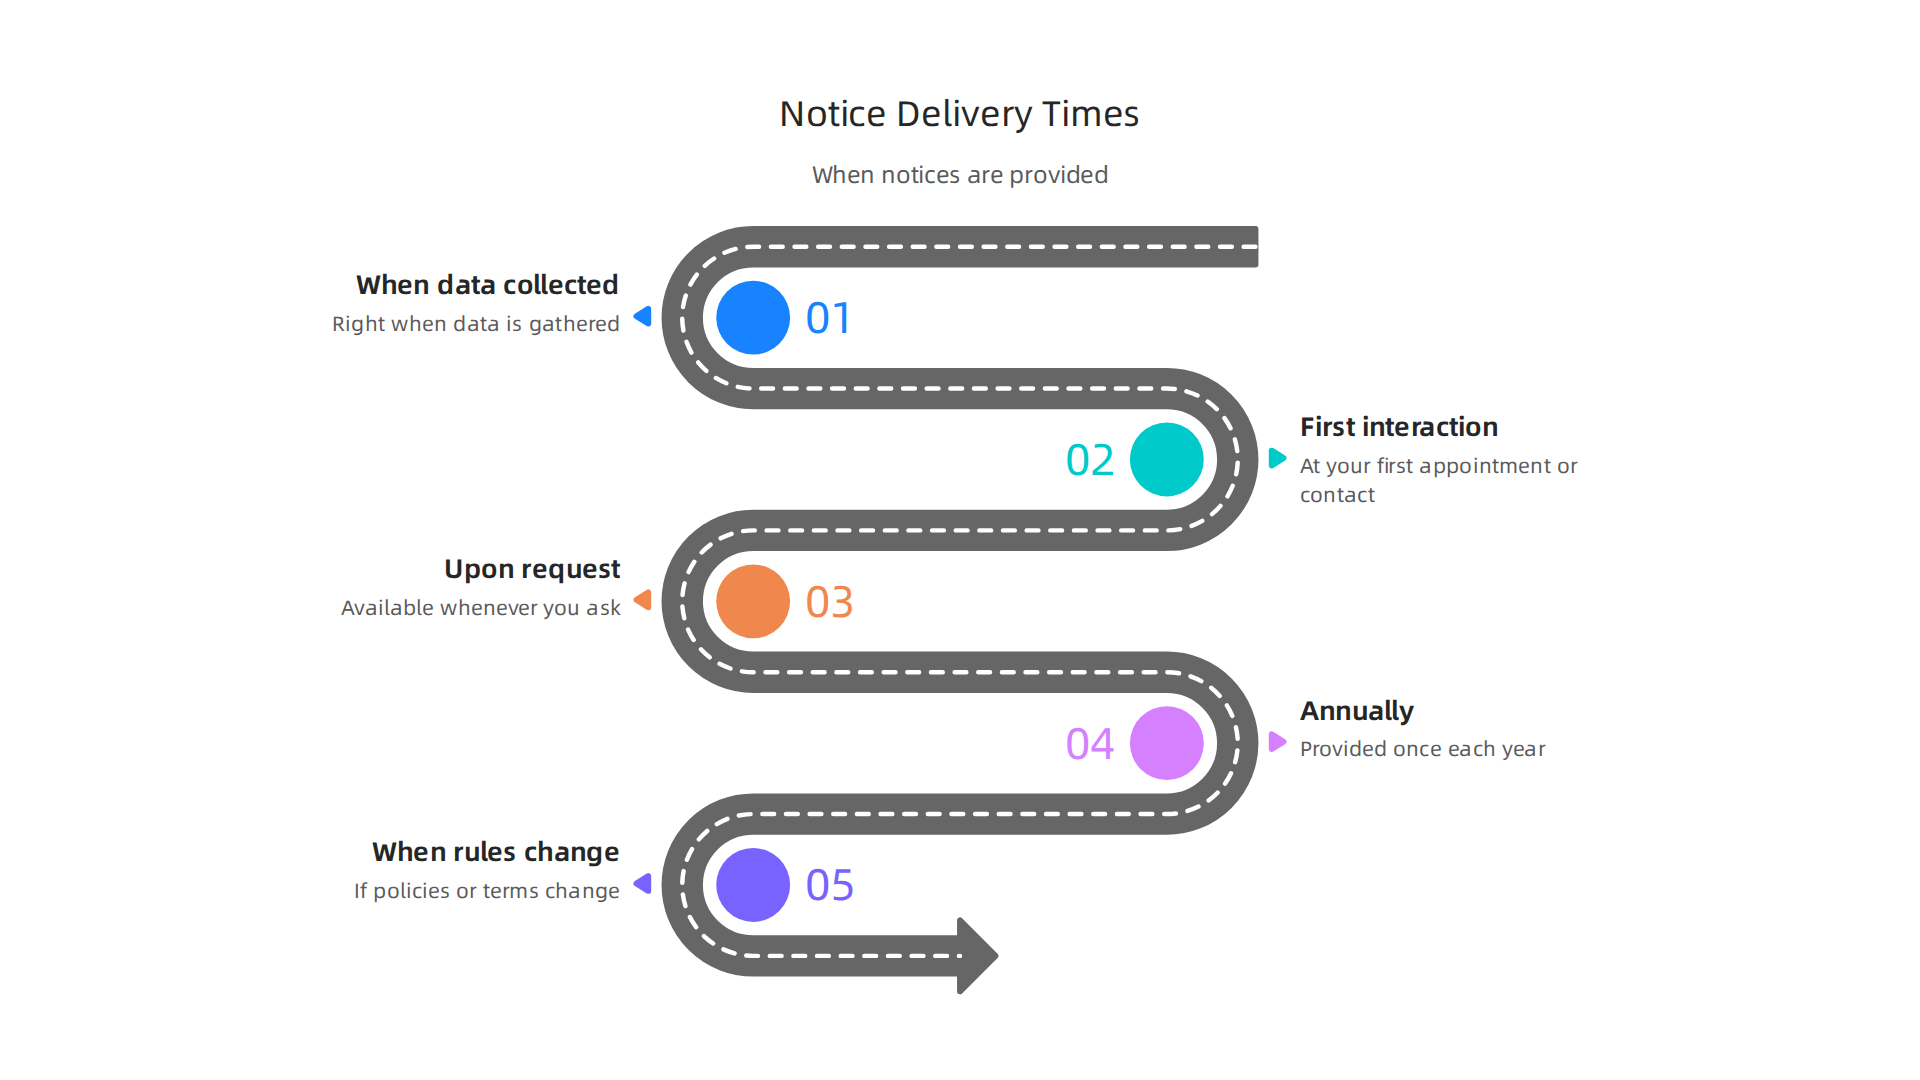
- When data is collected: Many laws say you should get a notice right when an organization first gathers your personal information. This could be when you sign up for a service online, fill out a form, or become a new customer.
- First interaction: For things like healthcare, you often get a notice when you have your first appointment or become a patient. HIPAA rules state that patients should get a HIPAA Notice of Privacy Practices on first contact with a healthcare provider.
- Upon request: You should always be able to ask for a copy of the privacy notice at any time.
- Annually: Some laws, like FERPA for schools, require notices to be given out once a year to parents and students. This ensures everyone stays updated on their rights regarding student records. The Department of Education provides annual notices guidance for schools to follow.
- When rules change: If an organization changes its privacy rules, they need to let you know. This is especially true for big updates, like the federal deadline in February 2026 for HIPAA Privacy Rule updates to support reproductive healthcare.
How you get the notice can also vary. You might see it:
- Posted in a public place, like a doctor's office or school lobby.
- Emailed to you, especially for online services.
- As part of an app, where you might agree to it when you first download or use the app.
- Given to you on paper to sign, like at a clinic.
These rules help protect your personal information and make sure organizations are open about how they handle your data. This helps prevent issues like privacy torts, where someone's privacy is wrongly invaded. Knowing when and how to get your notice of privacy practices is a key part of staying informed in 2026.
Enforcement and Penalties: What Happens If Notices Are Deficient
You now know what is the notice of privacy practices and when you should get it. But what happens if an organization does not give you a proper notice? Or if the notice is not clear enough? Actually, there are rules for this, and organizations can face serious trouble.
If a privacy notice is not good enough, or if it's not given out when it should be, a few things can happen:
- Official Warnings and Fines: Government groups, like the U.S. Department of Health and Human Services Office for Civil Rights (OCR) for HIPAA violations, can give warnings or even charge large fines. For example, if a healthcare provider does not follow the rules about how they handle patient information, they could face penalties. You can even file a complaint with the U.S. Department of Health and Human Services Office for Civil Rights if you believe your privacy rights were not respected.
- Corrective Actions: Beyond fines, organizations might be forced to change their privacy practices. This means they have to fix how they collect, use, and share your data to meet the law.
- Lawsuits from People: When notices are bad, it can make things worse if there's a data breach or other privacy problem. People whose data was affected might sue the organization. These are sometimes called privacy torts, which are legal claims for when someone's privacy is wrongly invaded. Having a weak privacy notice can make it much easier for people to win such lawsuits. Good data protection services solve the AI trust crisis by helping organizations handle data ethically and avoid these issues.
In short, a clear and correct notice of privacy practices is not just a nice-to-have. It's a must-have. It protects your personal information and helps organizations avoid big problems and costs in 2026.
Breaking Down the Notice: Language, Clarity, and AI-Specific Additions
A good notice of privacy practices is crucial, as we've learned. But what makes a notice truly good? It's all about how it's written and what it includes. In 2026, with new technologies like AI, this is more important than ever.
Making the Language Clear for Everyone
First, a notice of privacy practices must be easy for anyone to understand. This means using simple words and short sentences. Imagine you're explaining something to a friend, not a lawyer. Government rules often say these notices must be in plain language. For example, a good notice should clearly explain:
- How an organization uses your personal information.
- What rights you have over your data.
- How you can use those rights, like asking to see your information or changing it.
It should also include who to contact if you have questions or concerns. The goal is to make sure you truly know what you are agreeing to, without needing special help to read it. Experts agree that a privacy notice should clearly state things like why data is collected, how it's used, and who it's shared with How to write a privacy notice and what goes in it.
Special Rules for AI and Your Data
Now, let's talk about artificial intelligence (AI). Many companies use AI today, and this changes how they handle your data. Because AI systems learn from data, your privacy notice needs special sections that talk about how AI uses your information. These are called AI-specific disclosures.
Think about it this way: when you use an app or website, you give it information. If that company uses AI, it might use your information to train its AI models. This training can involve your words, pictures, or how you use the service. A clear notice will tell you if your information, even what might be considered proprietary data, will be used this way.
Here are some key things a good notice should explain about AI in 2026:
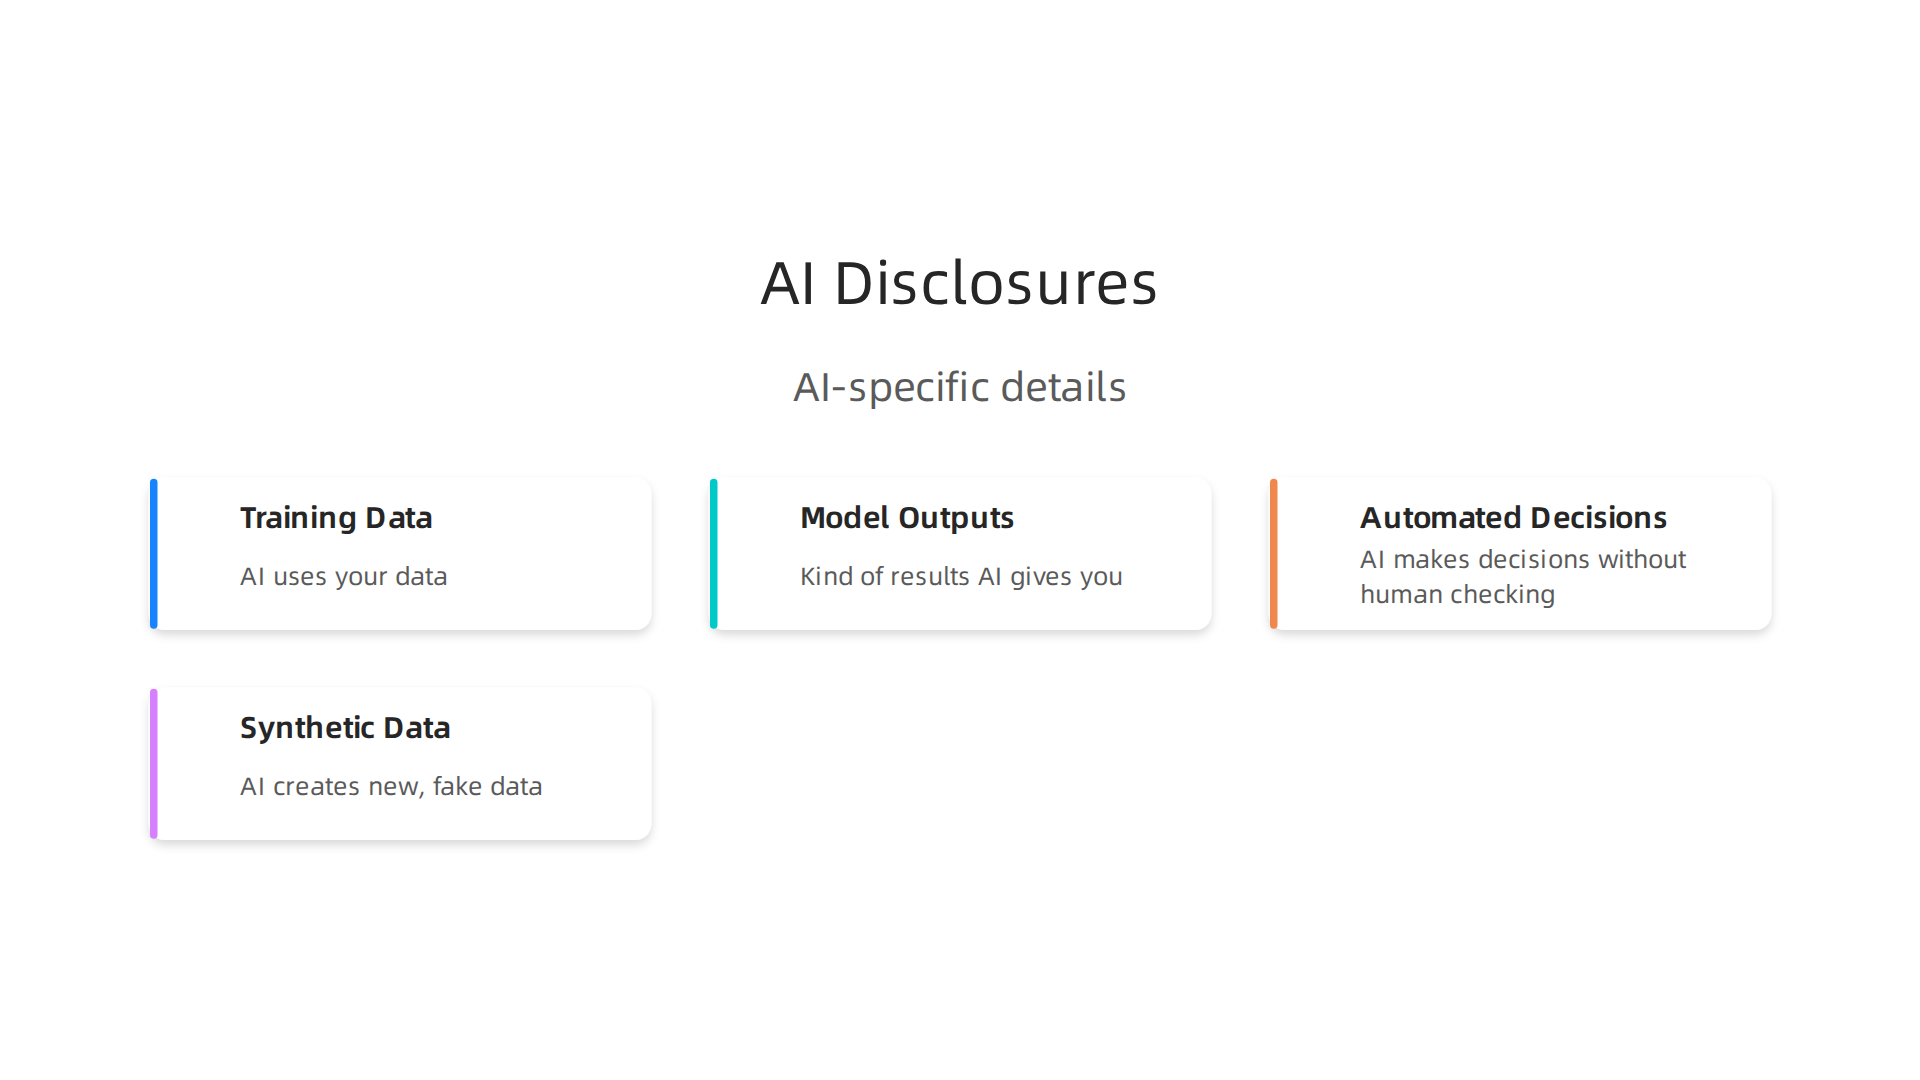
- Training Data: Does the AI use your data to get smarter? The notice should say if your inputs, like questions you ask or things you upload, help train the AI model.
- Model Outputs: What kind of results does the AI give you? And does it use your information to create those results?
- Automated Decisions: Does the AI make decisions about you without a human checking them? This could be for things like approving a loan, suggesting products, or even hiring. If so, the notice must explain how these decisions are made and if you can ask for a human review. Many new privacy policies in 2026 specifically require details on automated decision-making Privacy Policies are getting a massive upgrade in 2026!.
- Synthetic Data: Sometimes, AI creates new, fake data based on real data. The notice should say if your information helps create this "synthetic data" and how that data might be used.
These details are super important because they help you understand exactly how your personal data is involved with AI. Companies must be open about these practices. This helps to build trust and makes sure that AI is used in ways that respect your privacy. It's all part of making sure we can secure ethical AI with trustworthy data services.
When companies do not handle your data with care, or if their privacy notice is not clear, they can face big legal problems. These problems are often called "privacy torts" or can lead to lawsuits. Just like someone can sue you if you hurt them by accident, companies can be sued if they harm your privacy.
What are Privacy Torts?
Privacy torts are legal claims people can make if their personal privacy has been seriously violated. In 2026, these cases are becoming more common, especially with more data being collected. There are different ways a company might violate your privacy:
- Intrusion: This happens when a company secretly collects your private information without your permission, like monitoring you in a private space or getting into your personal accounts.
- Public Disclosure: This is when a company shares private facts about you with the public, even if the facts are true, but they are things that should have been kept secret.
- Misappropriation: This means a company uses your name or likeness for its own benefit without asking you first, often in advertising.
- False Light: This is when a company portrays you in a way that is misleading or untrue to the public, and it harms your reputation.
A good notice of privacy practices tells you exactly what a company will do with your information. If a company does something outside of what its notice says, or if the notice is confusing, it can open the door to these kinds of lawsuits. Courts are paying close attention to whether users got clear notice of terms when creating accounts, as seen in recent 2026 decisions Privacy Litigation Report: Takeaways From February 2026 Decisions.
How Notices Affect Lawsuits and Settlements
The clarity and completeness of a company's notice of privacy practices play a huge role when facing legal trouble. When a company is sued for something like a data breach, courts will look at whether they were clear about how they protected your information.
For example, imagine a large company like Advance Auto Parts had a data breach or if there was a Canva cyber attack where customer information was stolen. If their privacy notice didn't properly explain how they would protect your data, or if it was hard to understand, it could make things much worse for them in court. This could lead to a large settlement. In fact, privacy litigation reports show that courts are looking closely at how companies handle data and standing arguments in federal court Privacy Litigation Report: Takeaways From January 2026 Decisions.
A well-written notice can show that a company took steps to be open and honest with its users. This can help them defend against claims of negligence, where someone says the company was careless with their data. If a company collects your personal data and proprietary data without proper notice, or uses it in ways you didn't agree to, it can make lawsuits much harder to fight.
In 2026, companies are expected to do more than just have a basic privacy policy. They need to explain exactly how they collect, use, and protect information, especially with AI involved. Failing to do so can lead to expensive lawsuits and damage trust. To build better systems and avoid these risks, companies need to focus on ethical data practices from the start. Learn more about how data protection services solve the AI trust crisis.
Breach Settlements: Notice Failures, Mitigation, and Typical Settlement Dynamics
When a company's privacy notice is not clear, it does more than just cause legal issues. It can make those legal issues much more expensive, especially when a data breach happens. A poorly written notice of privacy practices can be used as proof that a company was careless. This makes it harder for them to defend themselves in court and often leads to larger payouts in settlements.
Imagine if there was an Advance Auto Parts data breach settlement or a Canva cyber attack where many customers' details were stolen. If the company's privacy notice did not properly explain how it keeps information safe, or if it used confusing language about how it handles sensitive or proprietary data meaning for its business, people could argue that the company misled them. This makes the company look bad and increases the money it might have to pay to settle the case.
Why Bad Notices Lead to Bigger Settlements
In court, if a company is facing a lawsuit due to privacy torts or a data breach, how clear their privacy notice was matters a lot. Lawyers for the affected people will point to vague or confusing language as evidence that the company failed to properly inform users. This can show a bigger problem with how the company handles privacy, not just a single mistake. This kind of evidence pushes companies to settle for more money to avoid a trial.
What’s Included in Typical Settlements
Data breach settlements often include several parts to help those affected. These usually are:
- Money for Victims: Sometimes, people who were harmed get direct payments.
- Credit Monitoring: Often, victims are offered free credit monitoring services for a few years. This helps them watch out for identity theft, which can happen after a data breach.
- Policy Changes: A big part of many settlements is forcing the company to fix its privacy and security problems. This includes making changes to their internal rules and how they handle data.
Notice Reform as Part of the Fix
A crucial part of these policy changes usually involves improving the what is the notice of privacy practices. Companies might be told to make their notices simpler, clearer, and easier to find. For instance, the Department of Health and Human Services provides model notices to help organizations, especially in healthcare, explain privacy practices in a way that people can understand. This is a must-do for many companies in 2026, as the rules about privacy notices keep getting stronger. For example, HIPAA rules required updates to privacy practices by February 16, 2026, to reflect new changes.
These updates ensure that individuals know their rights about their health information and how providers use it, as seen in the HIPAA Privacy Rule Final Rule to support reproductive health care. By improving their notice, companies show they are taking privacy seriously, which can help them avoid future lawsuits and rebuild trust with their customers. To build strong systems and avoid these privacy risks, companies need to focus on good data practices from the very beginning, like learning to prepare high-integrity data sets to build trustworthy AI.
Making privacy notices clear is a big step to avoid legal trouble, as we talked about earlier. But how do companies actually create and manage these important documents, especially now with new AI tools? It's about having good ways of working, from writing the notice to making sure people understand it and keeping it updated.
How to Write Good Notices for AI Services
When writing a privacy notice for services that use AI, companies need to be extra careful. It's not just about what data is collected, but how AI uses it. For example, a good AI privacy policy should explain what users type in (prompts), what they upload, what the AI gives back (outputs), any feedback given, and new information the AI creates from this. It also needs to say why this data is used, if other people or AI providers get to see it, if it helps train the AI, and how long the data is kept. Experts say that in 2026, companies need to explain clearly when and why AI is used, and how it fits into their services, like in hiring or customer help Expert’s guide to updating your privacy notices for AI.
Think about what information is used, what might happen because of it, if people are involved in the decisions, and how users can ask questions or make changes. This kind of detail goes into the main privacy notice. But sometimes, a shorter message right where a user interacts with the AI is also very helpful 15 AI Disclaimer Examples (2026). This helps people know exactly what's happening when they use an AI feature.
Companies also need to be clear about when AI makes decisions on its own. If an AI system makes choices that affect users, like setting prices or deciding who gets a service, the privacy notice must explain this clearly. It should say if the decision is fully automated, what it impacts, and if a person can review that decision AI Privacy Policy: An Informational Guide for Businesses in 2026. This helps build trust.
Making Sure People Understand
It's one thing to write a detailed privacy notice, but another to make sure people actually understand it. To do this, companies should test their notices with real users. This means asking people to read the notice and then seeing if they can explain what they just read in their own words. If users are confused, the notice needs to be made simpler and clearer. This helps avoid problems later on, like lawsuits that come from privacy torts or data breaches. Being transparent about AI use is a big deal in 2026, with privacy policies getting many upgrades to cover things like automated decision-making and training data Privacy Policies are getting a massive upgrade in 2026!.
Who Takes Care of the Notice and How It's Kept Up-to-Date
Good practices also mean having clear rules about who is in charge of the privacy notice.
This includes:
- Who owns it: Usually, a special team, like the privacy or legal team, is responsible for the notice.
- Getting approval: Before a notice goes live, different teams like legal, security, and product development need to agree on it.
- Updating the notice: Privacy notices should be reviewed often and updated as laws change or as the company uses new AI tools. Keeping a record of these changes, called an audit trail, is important. It shows regulators that the company is trying to follow the rules and can help if there's ever a legal issue. This process is key for Privacy as the Foundation of Responsible AI Governance.
Building strong systems for managing data is part of this. Learning about a security classification guide master data protection and AI access can help companies ensure their data practices support ethical AI. These steps help companies create notices that are not only legal but also truly helpful for users in understanding what is the notice of privacy practices in an AI-driven world.
Summary
This article explains what a Notice of Privacy Practices is, why it matters, and how organizations must craft and deliver it in 2026. It covers the core elements a good notice should include—what data is collected, why, how it's used and shared, your rights, and who to contact—and shows how notices vary across healthcare, government, and commercial platforms. The piece highlights updated legal obligations (for example, HIPAA and FERPA), timing and delivery rules, and how AI changes disclosure needs by requiring transparency about model training, automated decisions, and synthetic data. It also outlines the enforcement risks and how weak notices can increase fines and settlement costs after breaches. Finally, it gives practical guidance on writing plain-language notices, testing comprehension, assigning ownership, and keeping notices current so organizations can build trust and reduce legal risk.
Related Blogs
No Similar Blogs found
